Analysis library
Clear analysis for consequential cybersecurity decisions.
Browse independent analysis of cybersecurity architecture, business risk, resilience, AI, and emerging technology.
-
Weekly Cybersecurity Report: Binance Theft, UNM Health Disruption, and Cisco SD-WAN Exploitation — October 26–November 1, 2026
Patient-care disruption, a state-attributed cryptocurrency theft, exposed cloud secrets, compromised developer platforms, and exploited infrastructure shaped an unusually active week.
-
Weekly Cybersecurity Report: PHP2Shell, LiteLLM, Railway, and Storm-0940 — October 19–25, 2026
PHP2Shell exploitation, compromised LiteLLM releases, exposed Railway secrets, and attacks on trusted application and network control planes demand investigation beyond…
-
Weekly Cybersecurity Report: French Refrigeration Attacks, ConnectWise Cloud Backup, and Exploited Edge Systems — October 12–18, 2026
Cyberattacks disrupted French refrigeration systems, compromised ConnectWise application identities, and exploited privileged Ivanti, Cisco, BeyondTrust, and PAN-OS platforms.
-
Weekly Cybersecurity Report: October 5–11, 2026 — SonicWall, AhsayCBS, Flax Typhoon, and AI Agent Incidents
Rapid targeting of SonicWall, exploitation of AhsayCBS, a Flax Typhoon disruption, identity-data exposure, and AI agents crossing external boundaries shaped…
-
Weekly Cybersecurity Report: September 28–October 4, 2026 — FortiMail, SD-WAN, and Exposed GitHub Secrets
Active exploitation of enterprise control planes, unsafe AI-agent behavior, persistent credential exposure, and critical-infrastructure attacks demand faster investigation, containment, and…
-
Weekly Cybersecurity Report: September 21–27, 2026 — NetScaler, EvilTokens, and NIST’s OT Draft
Exploited edge platforms, adaptive enterprise attacks, cloud-identity abuse, AI-agent boundary failures, and updated OT guidance drive this week’s leadership priorities.
-
Weekly Cybersecurity Report: Exploited Trust Controls, Supply-Chain Exposure, and AI Agent Boundaries
Exploited security controls, trusted-script compromise, maritime cyber incidents, developer targeting, and AI-agent weaknesses put enterprise trust boundaries under scrutiny.
-
Stop Treating Phishing Click Rate as a Resilience Metric
New research reinforces an old warning: phishing click rate cannot prove resilience. Leaders need evidence of credential protection, reporting, and…
-
Weekly Cybersecurity Report: Control-Plane Exploits, Agentic Attacks, and EU Reporting
Exploited control planes, faster AI-enabled attacks, evolving identity fraud, and new EU product-security reporting obligations shaped this week’s leadership decisions.
-

The FBI Cyber Strategy Changes the Incident Contract
The FBI’s new cyber strategy promises faster victim support, deeper partnerships, expanded OT expertise, and AI-enabled operations. Enterprises must build…
-
Weekly Cybersecurity Report: Trusted Infrastructure, AI Credentials, and Quantum Readiness
Trusted enterprise platforms faced rapid exploitation, AI services exposed concentrated credentials, and new guidance sharpened decisions on post-quantum migration and…
-
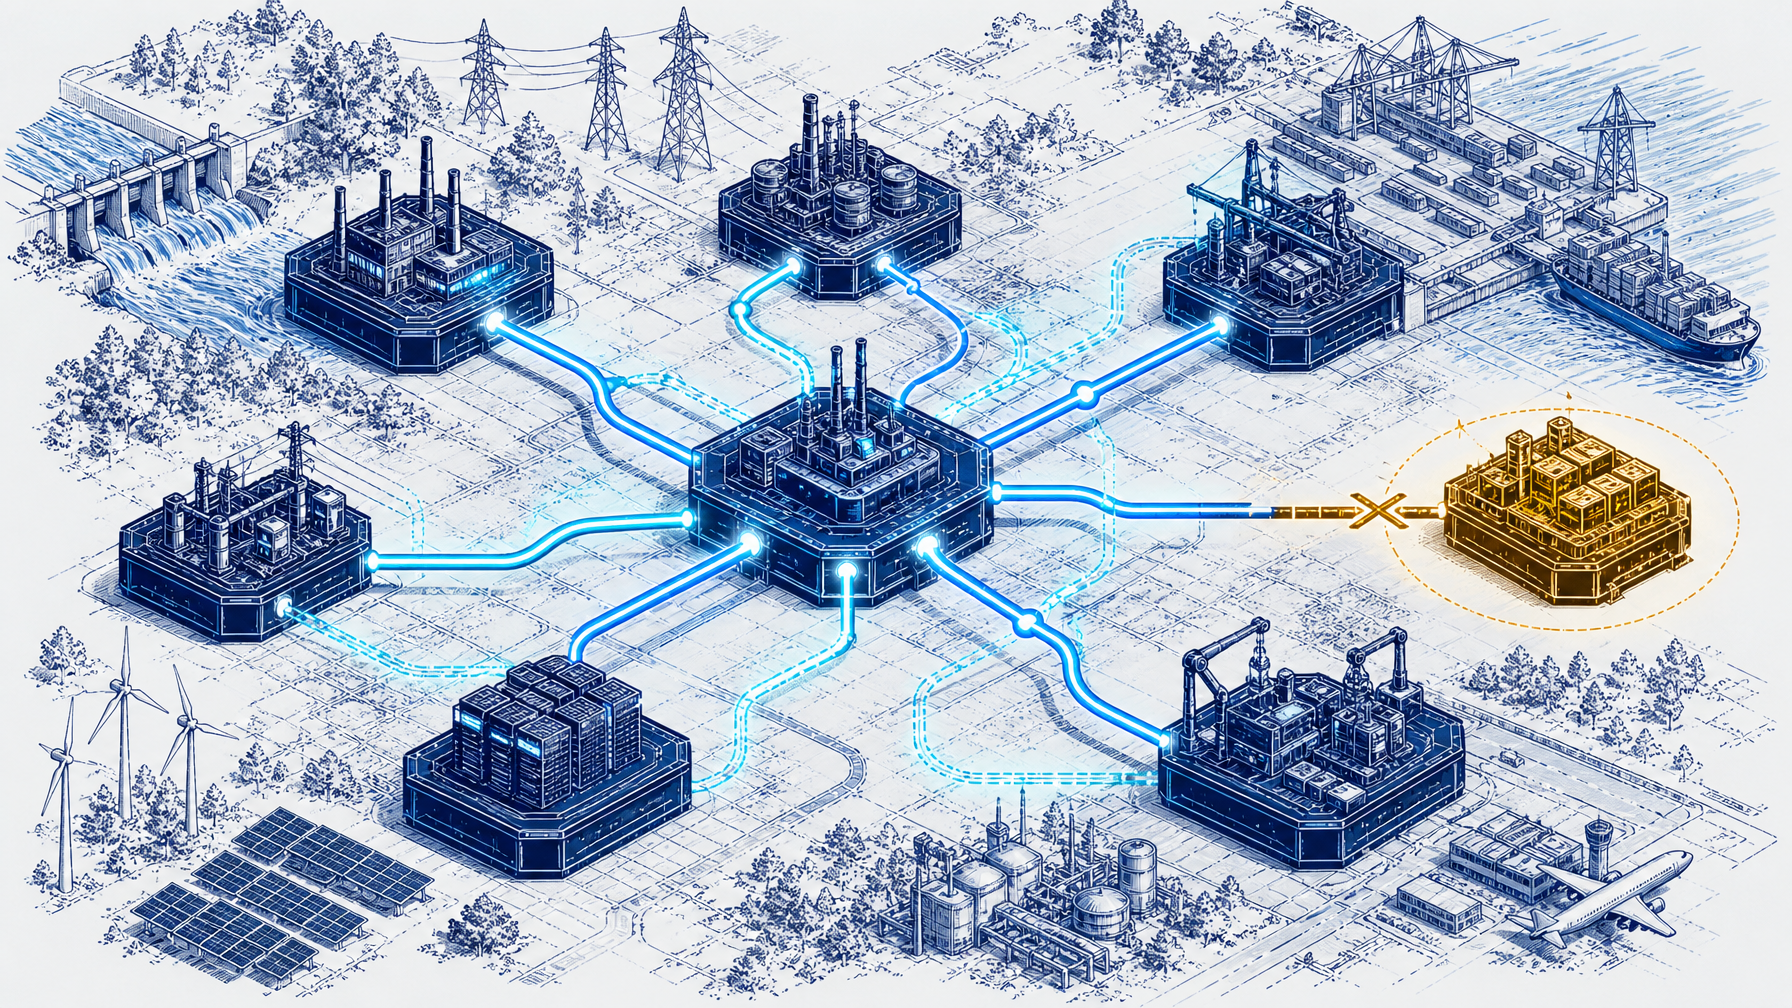
UK Vendor Directions Turn Procurement Into Architecture
Proposed UK powers could force critical-infrastructure operators to restrict or remove vendor technology. The practical response is dependency knowledge, safe…