Shawn Maschino
Black Hat USA 2026: The Security Boundary Is the Story
An executive review of Black Hat USA 2026 covering agentic AI, concentrated trust, hardware risk, resilience, and the decisions leaders should make now.
Cloud Security Accountability Cannot Stop at the Contract
Recent GAO findings reveal a broader cloud lesson: provider contracts matter, but accountability depends on evidence, tested response, and enforceable service expectations.
Your Security Plan Should Be an Operating Contract, Not an Audit Artifact
NIST’s updated system-planning guidance gives leaders an opportunity to connect security, privacy, and supply-chain decisions to business ownership, evidence, and change.
Weekly Cybersecurity Report: OT Exposure, RMM Exploitation, and AI Agent Risk
Water-sector intrusions expanded, N-central required a superseding hotfix, and new research exposed consequential weaknesses in enterprise AI agents and connected infrastructure.
Weekly Cybersecurity Report: PLM Extortion, Agentic Defense, and AI Security
A leadership brief on healthcare-data exposure, active Windchill exploitation, agentic cyber defense, and the emerging AI-security ecosystem.
Securing AI Agents: Moving From One-Time Approval to Continuous Assurance
Why this matters now Organizations are beginning to use AI agents for activities that extend beyond generating or summarizing information. Depending on how they are configured, agents can retrieve sensitive data, call APIs, modify records, generate code, initiate workflows, and perform actions across business systems. This creates a material change in risk. A chatbot generally…
Modernizing Enterprise Security Architecture Beyond Framework Compliance
A practical model for connecting business outcomes, risk decisions, security capabilities, architecture patterns, controls, evidence, and measurable improvement.
Autonomous AI as a Cyber Threat: What Leaders Should Prepare For
Agentic AI can plan, use tools, and adapt across multiple steps. Leaders should constrain identity, authority, data, execution, telemetry, and recovery.
Short-Lived TLS Certificates: Preparing for the 47-Day Lifecycle
Publicly trusted TLS certificates are moving to a 47-day maximum by 2029. Prepare with end-to-end discovery, issuance, deployment, validation, and renewal automation.
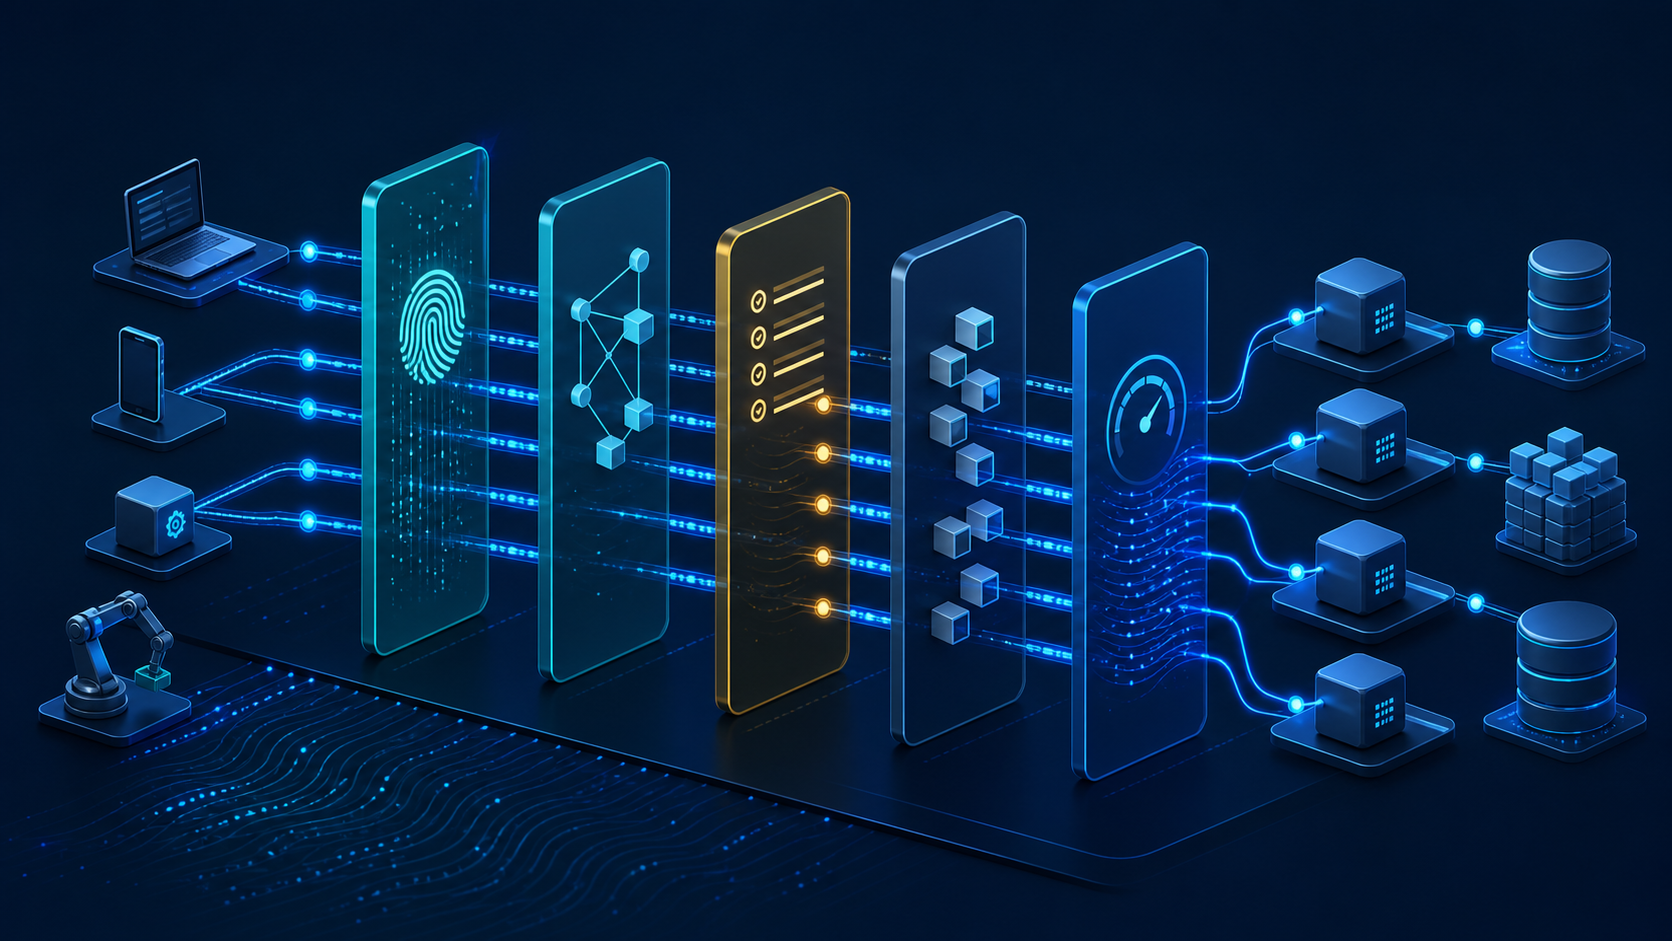
API Security Is Business Security: Architecture Priorities for Modern Enterprises
Modern API security depends on inventory, fine-grained authorization, abuse-resistant business flows, safe third-party consumption, and end-to-end transaction visibility.