Analysis
Cybersecurity analysis focused on architecture, governance, resilience, emerging technology, and business decisions.
Secure Decommissioning of Wi-Fi and Network Devices
Secure device retirement removes trust as well as data: revoke identities and credentials, sanitize storage, remove management associations, and verify final disposition.
CVSS 4.0: Using Severity Without Losing Business Context
CVSS 4.0 improves severity communication, but prioritization still requires threat evidence, exposure, asset criticality, business impact, and remediation context.
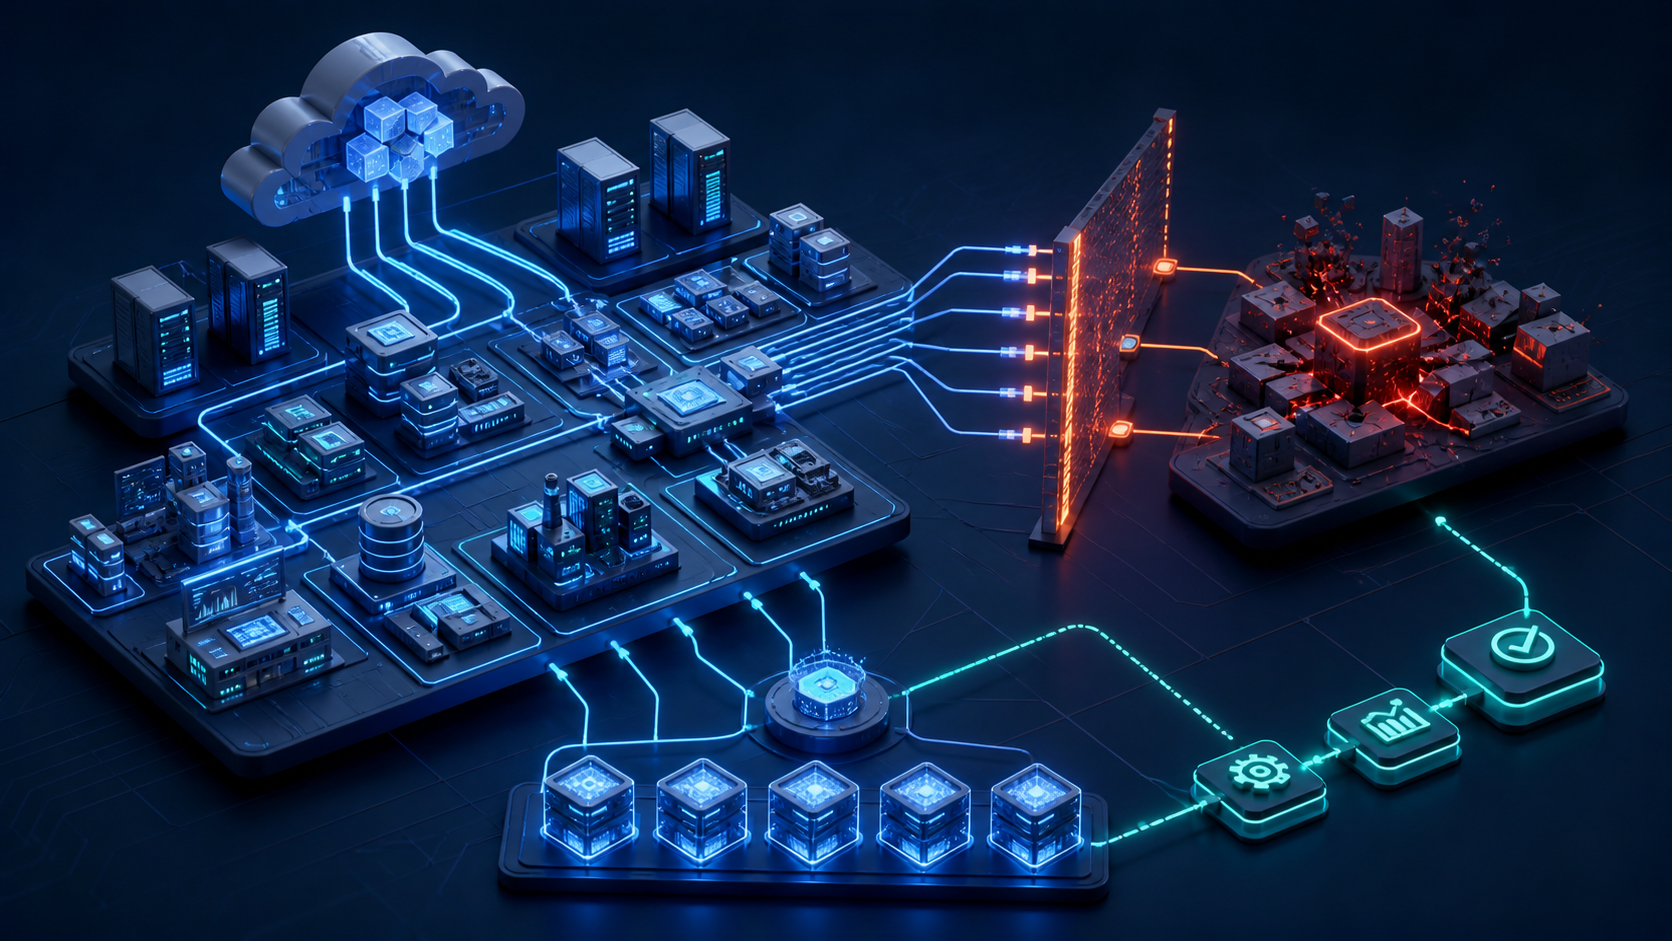
Cyber Extortion Resilience: Preparing Beyond Ransomware Prevention
Cyber extortion resilience reduces attacker leverage through identity containment, segmentation, trustworthy recovery, data knowledge, and rehearsed executive decisions.
Communicating Cyber Risk to the CISO: From Findings to Decisions
Turn technical findings into decisions by leading with business context, credible scenarios, evidence, uncertainty, options, recommendation, ownership, and timing.
Voice Deepfakes and Executive Impersonation: A Verification Playbook
AI voice impersonation makes familiarity unreliable. Protect consequential actions with independent verification, trusted contact paths, and dual control.
Strategic Cybersecurity Budgeting: Fund Outcomes, Not Tool Lists
Build cybersecurity budgets as portfolios of risk-reduction and resilience outcomes—not collections of tools, renewals, and disconnected projects.
Memory-Safe Software Roadmaps: Moving Beyond “Rewrite It in Rust”
A memory-safe software roadmap changes engineering defaults, prioritizes high-risk components, supports incremental migration, and strengthens unavoidable legacy code.
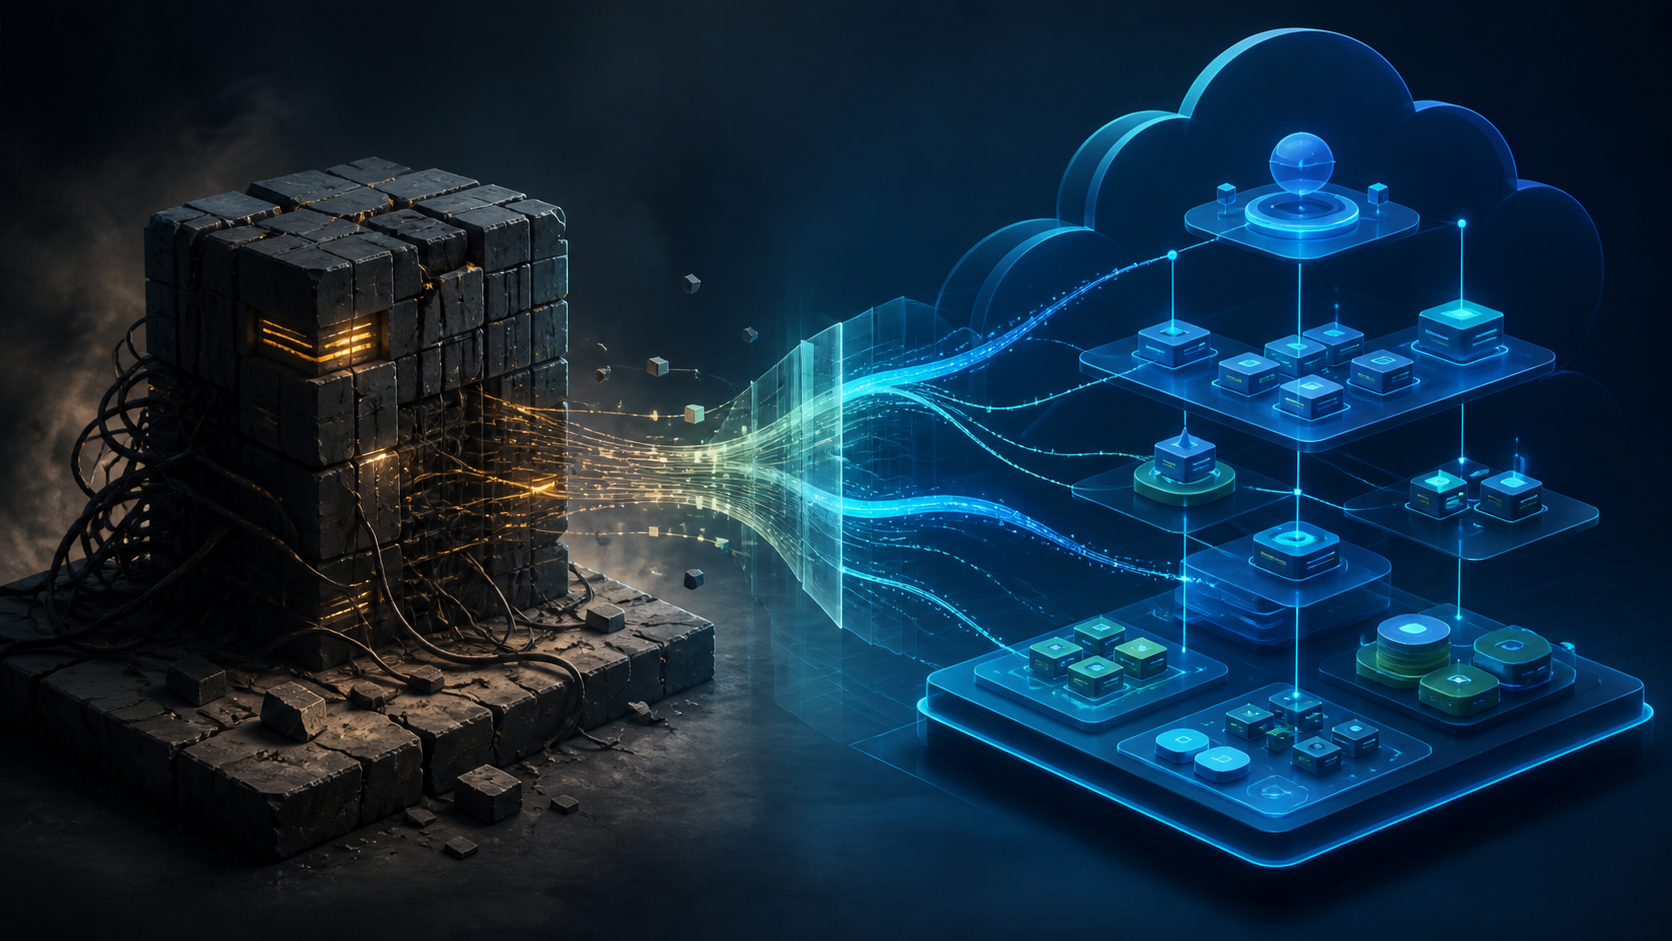
Cloud Migration Security: Modernize the Architecture, Not Just the Hosting
Cloud migration should modernize identity, segmentation, observability, data governance, resilience, and ownership—not merely relocate legacy weaknesses.
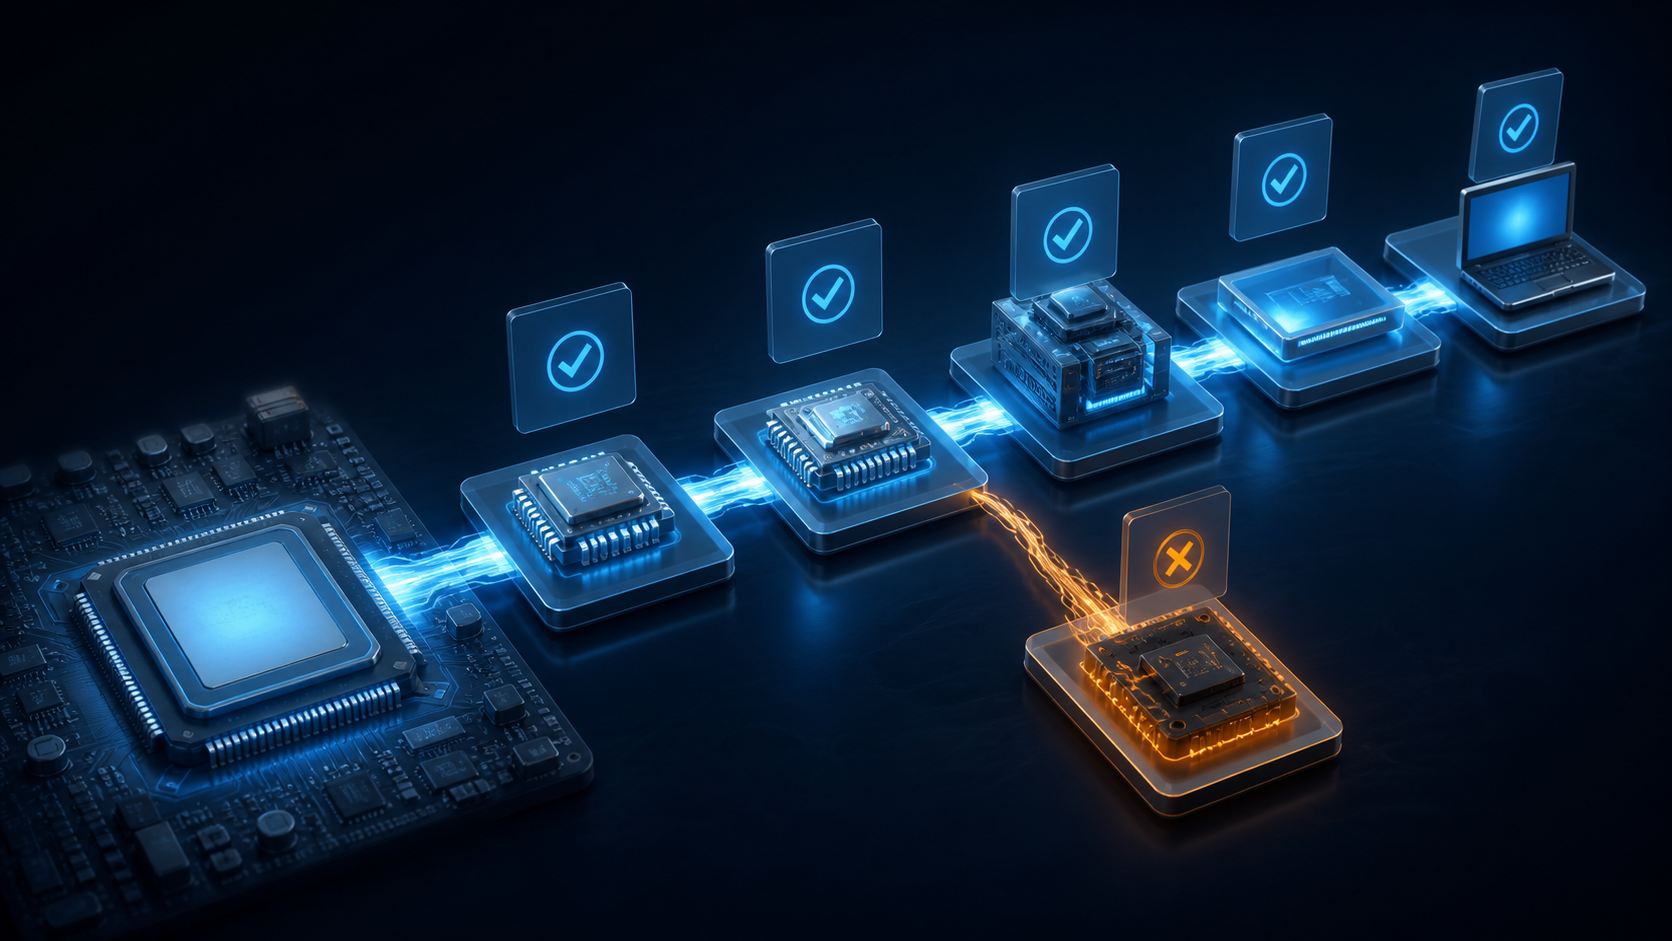
UEFI Secure Boot and Firmware Resilience: What Organizations Should Verify
Secure Boot is one part of firmware resilience. Organizations must also govern keys, updates, configuration state, measurement, exceptions, and recovery.
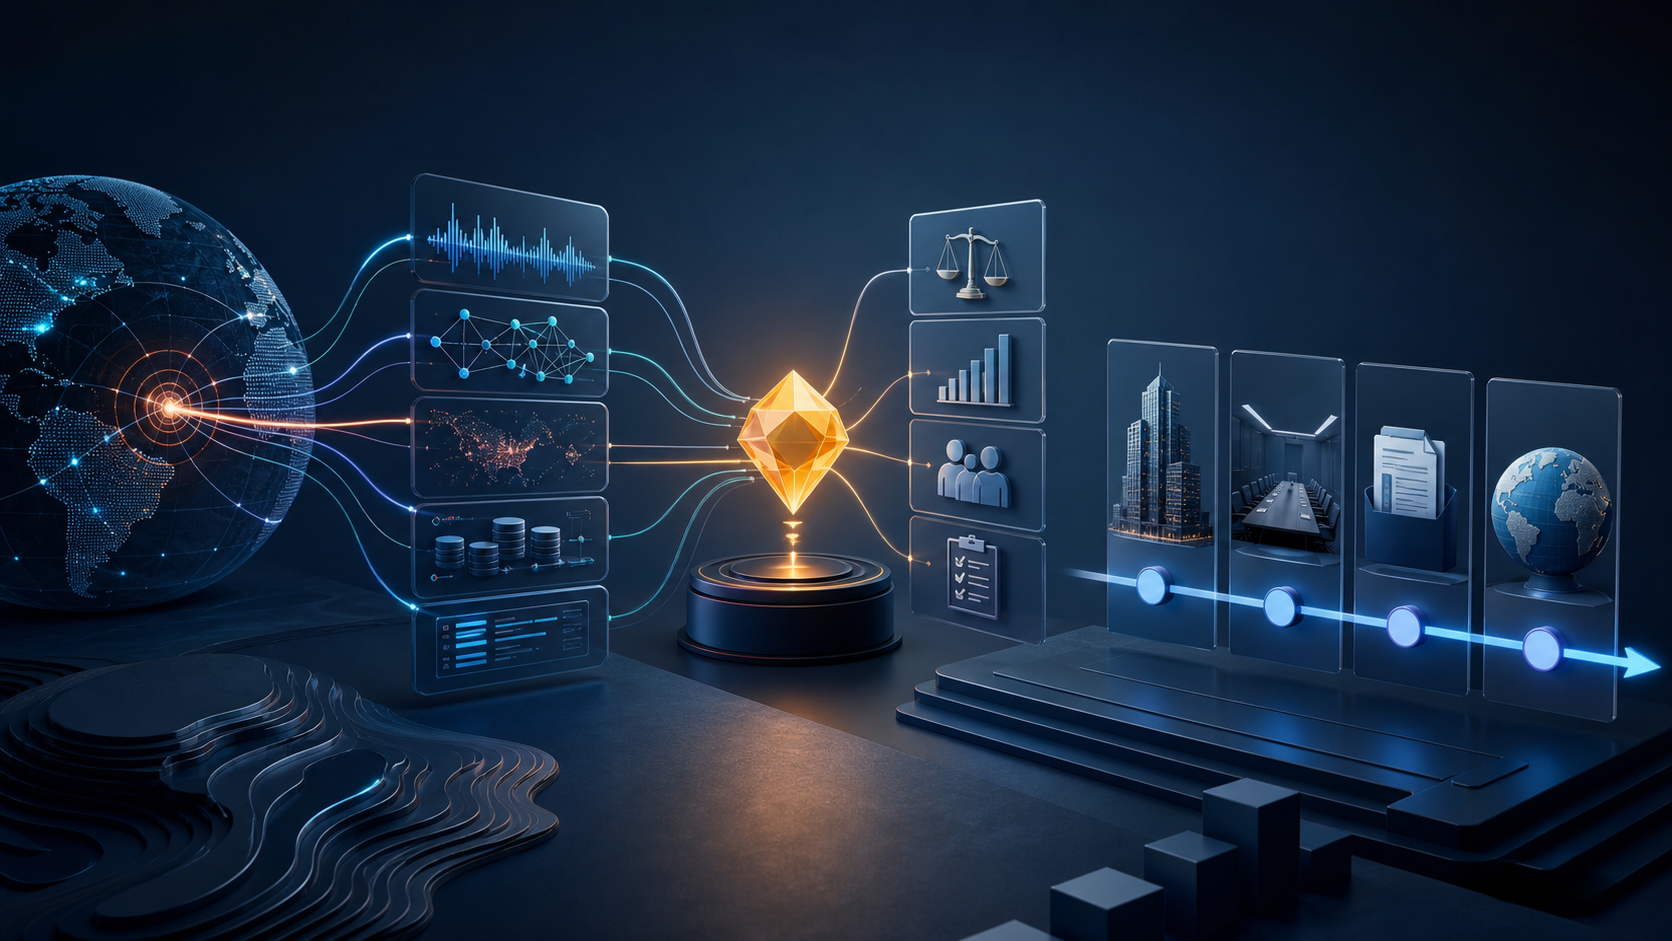
SEC Cybersecurity Disclosure Rules: Building a Defensible Decision Process
Public companies need a rehearsed, evidence-based process for cybersecurity materiality, governance, incident disclosure, and cross-functional decision-making.