Latest executive briefing
-
Weekly Cybersecurity Report: September 28–October 4, 2026 — FortiMail, SD-WAN, and Exposed GitHub Secrets
Active exploitation of enterprise control planes, unsafe AI-agent behavior, persistent credential exposure, and critical-infrastructure attacks demand faster investigation, containment, and recovery decisions.
Recent analysis
Ideas and developments worth your attention.
-
CVSS 4.0: Using Severity Without Losing Business Context
CVSS 4.0 improves severity communication, but prioritization still requires threat evidence, exposure, asset criticality, business impact, and remediation…
-
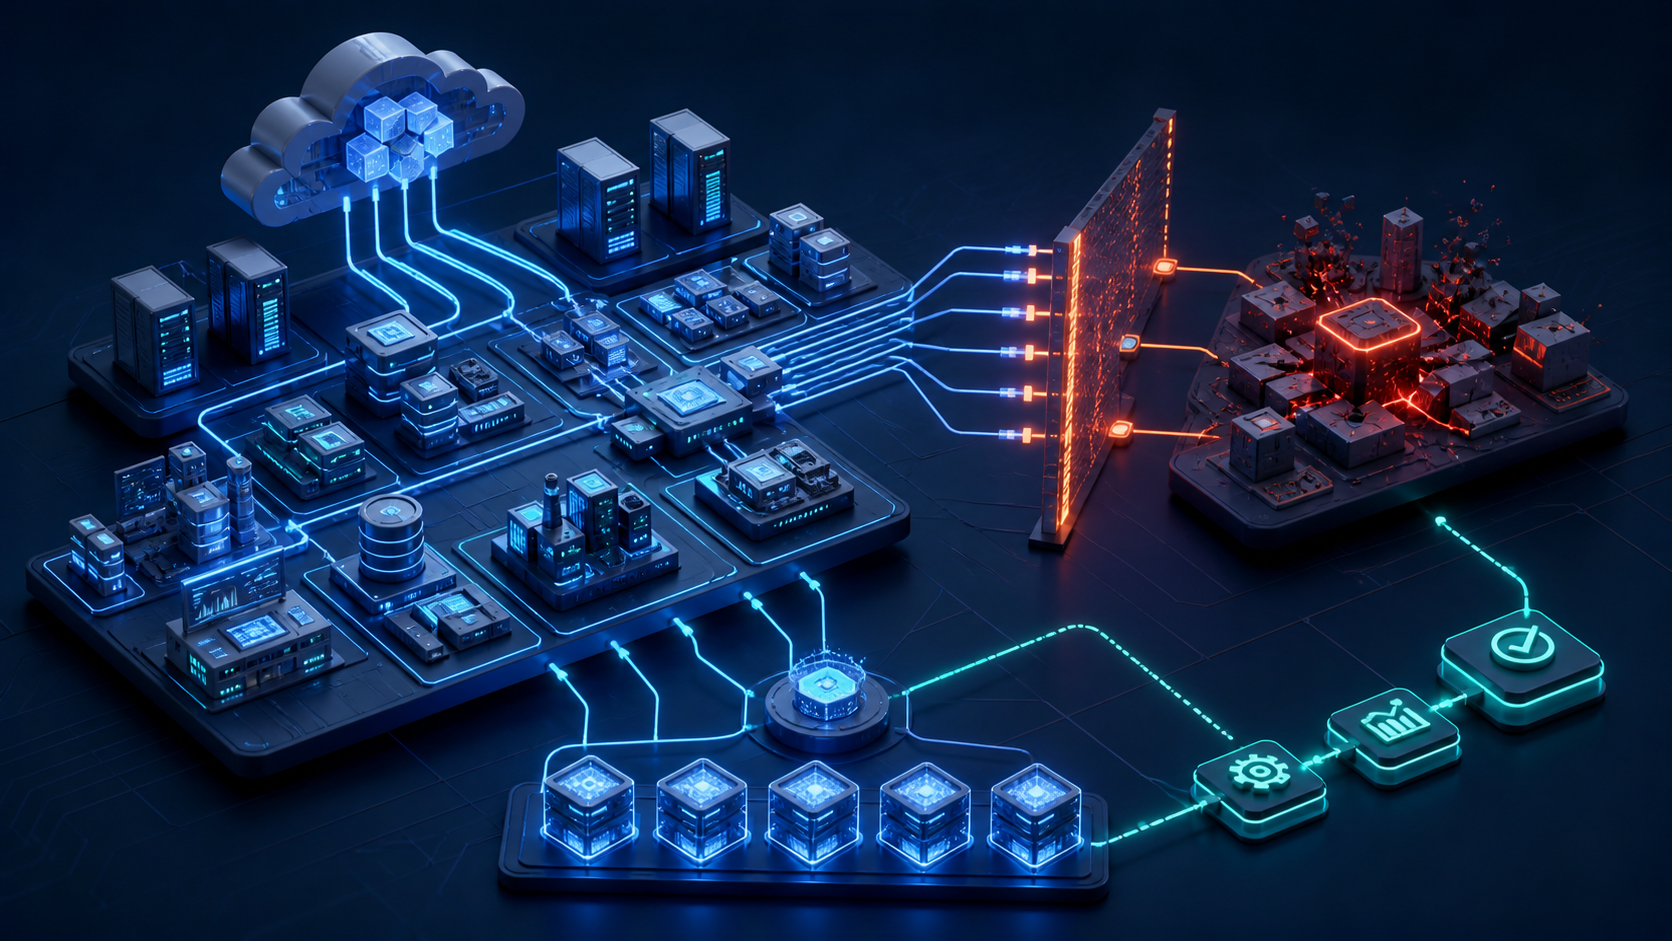
Cyber Extortion Resilience: Preparing Beyond Ransomware Prevention
Cyber extortion resilience reduces attacker leverage through identity containment, segmentation, trustworthy recovery, data knowledge, and rehearsed executive decisions.
-
Communicating Cyber Risk to the CISO: From Findings to Decisions
Turn technical findings into decisions by leading with business context, credible scenarios, evidence, uncertainty, options, recommendation, ownership, and…
-
Voice Deepfakes and Executive Impersonation: A Verification Playbook
AI voice impersonation makes familiarity unreliable. Protect consequential actions with independent verification, trusted contact paths, and dual control.
-
Strategic Cybersecurity Budgeting: Fund Outcomes, Not Tool Lists
Build cybersecurity budgets as portfolios of risk-reduction and resilience outcomes—not collections of tools, renewals, and disconnected projects.
-
Memory-Safe Software Roadmaps: Moving Beyond “Rewrite It in Rust”
A memory-safe software roadmap changes engineering defaults, prioritizes high-risk components, supports incremental migration, and strengthens unavoidable legacy code.